
Identity Is More Than Recognition
Identity Is More Than Recognition
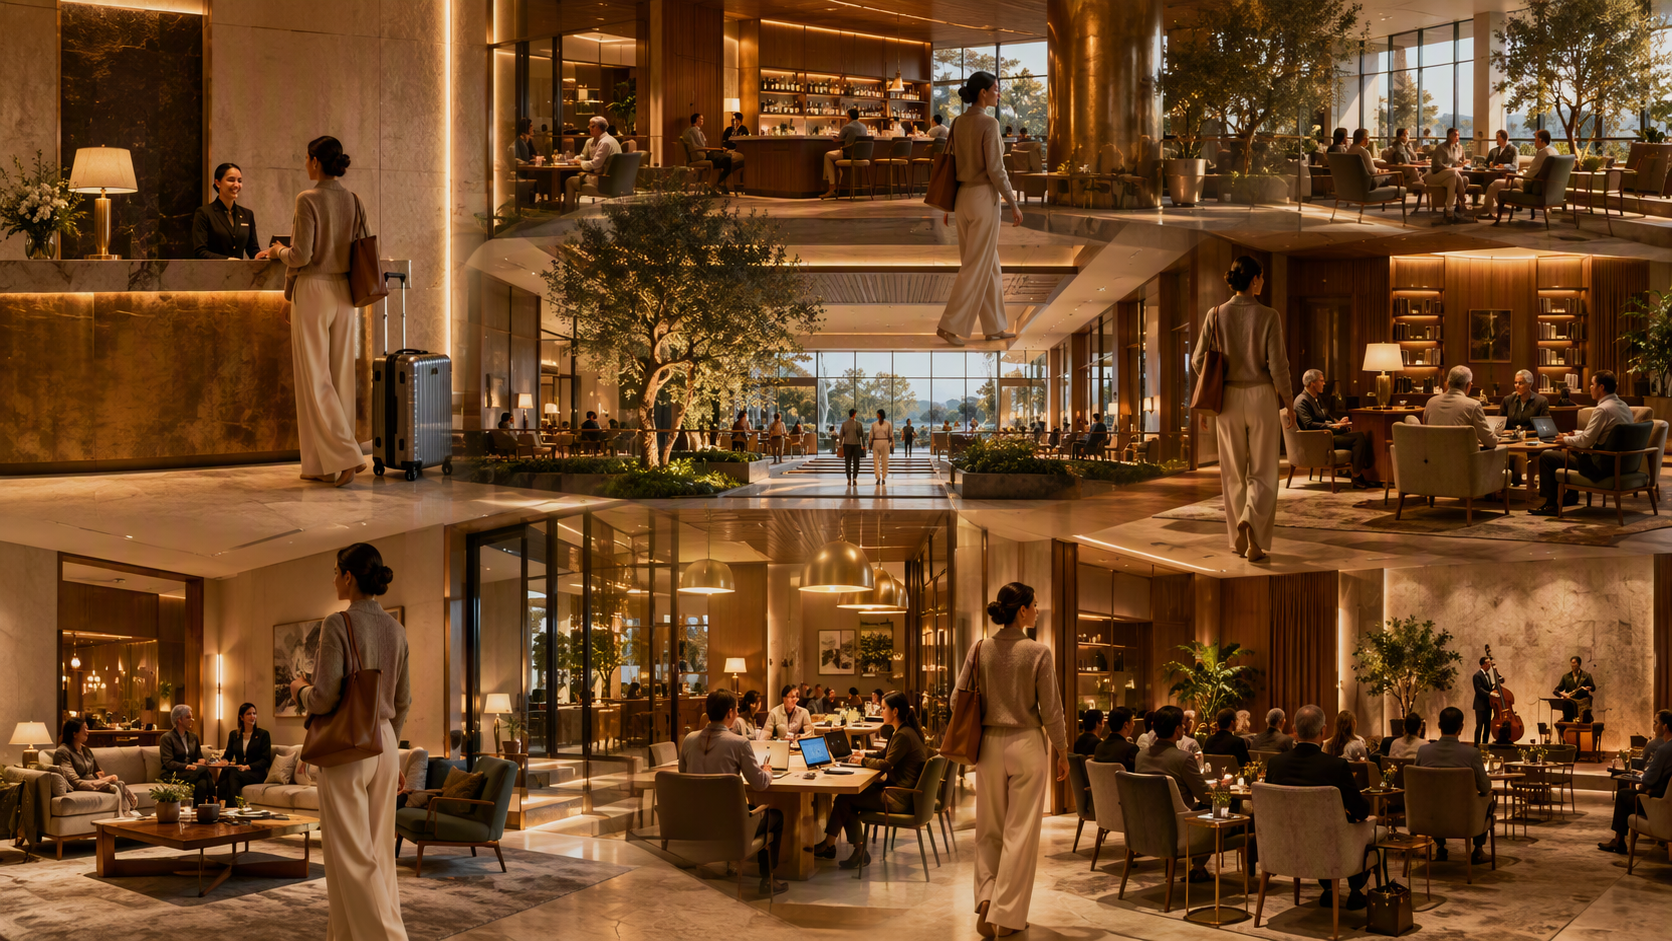
A few years ago, I found myself sitting in a hotel lobby waiting for a colleague to arrive. It wasn't a particularly memorable trip, and at the time I wasn't thinking about intelligent environments, governance frameworks, or identity models. I was simply watching people come and go while I waited. A guest approached the front desk, provided a name, and within seconds the reservation appeared on the screen. The process was smooth and familiar. A few minutes later, another guest stepped up and went through what appeared to be the same process. This time, however, the conversation lasted longer. There were questions about room access, amenities, benefits associated with the reservation, and services that were available to some guests but not others.
As I sat there, it struck me that both interactions started with exactly the same question. The hotel needed to determine who was standing in front of the desk. Yet once that question was answered, a completely different set of decisions immediately followed. Knowing a guest's identity didn't automatically determine what room they could access, what services they could use, or what information could be shared. Recognition solved one problem, but it revealed several others. The hotel knew who these people were. The more important challenge was determining what that relationship meant.
That realization stayed with me long after I forgot the hotel itself. In fact, the more I've worked with intelligent environments, the more I've come to believe that many conversations about identity quietly confuse two very different concepts. We often talk as though recognition and authorization are the same thing. If a system can identify a person, we assume it somehow knows what should happen next. But those are entirely different questions. One asks who someone is. The other asks what is appropriate.
Our homes make this distinction feel almost effortless, which is one reason we don't always notice it. When someone arrives at my home, I rarely think about identity management or authorization models. David doesn't need to explain why he's there. Maisey certainly doesn't. Friends, family members, guests, and house sitters all arrive with relationships that carry meaning before anyone walks through the door. A dinner guest is welcomed differently than a house sitter. A family member has a different role than a contractor. The distinction doesn't feel technical because we manage it instinctively. The Home doesn't simply recognize the individual. The Home understands the relationship.
What fascinates me is how often we lose that intuition when we move from Homes into shared environments. The moment technology becomes involved, conversations frequently focus on recognition. We discuss credentials, badges, facial recognition systems, mobile applications, reservations, memberships, and authentication methods. Those capabilities matter, but they only answer the first question. Once recognition succeeds, the real work begins.
Think about checking into a hotel after a long day of travel. The hotel recognizes your reservation immediately. It knows your name, your loyalty status, your stay history, and perhaps even some personal preferences. On the surface, it may seem as though the identity problem has been solved. Yet recognition alone doesn't determine whether you have access to a concierge lounge, whether a premium service is included with your reservation, or whether information should be discussed openly in a crowded lobby. The hotel may know exactly who you are and still need to make decisions about what is appropriate.
Once I began looking for this pattern, I saw it everywhere. Membership organizations encounter it daily. Assisted-living communities navigate it constantly. Mixed-use developments, hotels, entertainment venues, and community spaces all face the same reality. The environment isn't merely asking, "Who is this person?" The environment is asking, "What does this person's relationship to this space mean right now?" Those are fundamentally different questions, and they often produce very different answers.
One of the most valuable lessons I've learned is that identity frequently has less to do with the individual than with the role the individual occupies at a particular moment. The same person may participate in an environment through multiple relationships simultaneously. A hotel guest may also be attending a conference. A resident may also serve as a volunteer. An employee may also be a customer. A contractor may have authority in one area while being unauthorized in another. None of those scenarios require a different identity. What changes is the relationship. And more often than not, it is the relationship that determines what should happen next.
That observation has made me increasingly cautious when discussions focus exclusively on recognition technology. Better recognition can absolutely improve experiences. It can reduce friction, eliminate repetitive tasks, and make environments feel more welcoming. But recognition is only the starting point. The most important decisions occur after identity is established. Once an environment knows who someone is, it still has to determine what information should be shared, what access should be granted, what responsibilities exist, and who remains accountable for those decisions.
The complexity grows even further when information begins traveling with identity. Many of us appreciate continuity. A returning hotel guest may enjoy not having to restate preferences. A community member may value recurring reservations or activity history. An assisted-living resident may benefit from systems that preserve independence while still providing support when needed. These experiences can create tremendous value. Yet they also force us to ask additional questions. Who should have access to that information? How long should it be retained? What purpose does it serve? Under what circumstances should it be used? Recognition may provide context, but context doesn't eliminate the need for judgment.
The more I think about these questions, the more convinced I become that trusted environments are not built on recognition alone. Human Trust doesn't emerge because a system successfully identifies someone. Trust emerges because the environment behaves appropriately once that recognition occurs. A person shouldn't lose privacy simply because they are known. Information shouldn't be exposed merely because it exists. Access shouldn't automatically follow recognition. The environment must still understand what is true, what permissions exist, what responsibilities accompany those permissions, and what stewardship requires in that situation.
Throughout my career, I've learned that many disagreements in technology are actually disagreements about vocabulary. People use the word identity when they mean recognition. They use the word known when they mean authorized. They use the word personalized when they really mean trusted. These distinctions may seem small, but they have enormous consequences. Once we separate recognition from authorization, environments become easier to design, govern, and reason about. We can recognize someone without becoming intrusive. We can preserve continuity without oversharing information. We can acknowledge a relationship without assuming unlimited authority.
Perhaps that's why the questions that occupy my mind today are different than they once were. I'm no longer particularly fascinated by whether a system can recognize someone. Technology will continue to improve. Recognition will become faster, cheaper, and more accurate. Those advances feel almost inevitable. The questions that matter most begin after recognition succeeds. What should the environment do? What should it know? What should it remember? What should it reveal? What should it authorize?
Those are the decisions that determine whether a space feels respectful, trustworthy, and human-centered.
Recognition begins the conversation.
The environment's behavior determines how the conversation ends.
Recognition is not authorization. Knowing who someone is doesn't automatically determine what they're allowed to do, what information may be shared, what obligations exist, or what behavior is appropriate. Identity provides context. Trustworthy environments still require judgment, stewardship, and the discipline to understand the difference.